Google Workspace: single sign-on
Let people log in to MuchSkills through your Google Workspace, with access controlled from the Google Admin console. You add a custom SAML app in Google, connect it on the Security & SAML screen in MuchSkills, test it, and then decide whether to enforce it.
- Who
- A MuchSkills Owner or Admin, with a Google Workspace super administrator
- How it connects
- Support adds your email domain, then you finish in Settings › Security & SAML
- Standard
- SAML 2.0
- Plans
- Included in all plans
How to
Before you start
- In MuchSkills: the Owner or Admin role. Only these roles can open the Security & SAML screen.
- In Google Workspace: a super administrator in the Google Admin console.
- Your email domains. List every domain your people log in with. Support adds them for you in step 1.
- Matching email addresses. MuchSkills recognises people by email. Each person's primary Google email should be the address they use for MuchSkills.
- Somewhere to put the metadata. Google gives you its IdP metadata as a file. Decide whether you host it at an HTTPS address you control, or send it to support (step 7).
Steps
In MuchSkills
- Ask support to add your email domains. Email support@muchskills.com or use the chat in MuchSkills. List every domain your people use. When the domains are added, they appear under Email domains on Team/Org › Settings › Security & SAML, which says No domain added until then.
- Copy your SSO URL. On the same screen, copy the SSO URL. It starts with
https://app.muchskills.com/auth/saml/followed by your organisation's ID. Keep this tab open.
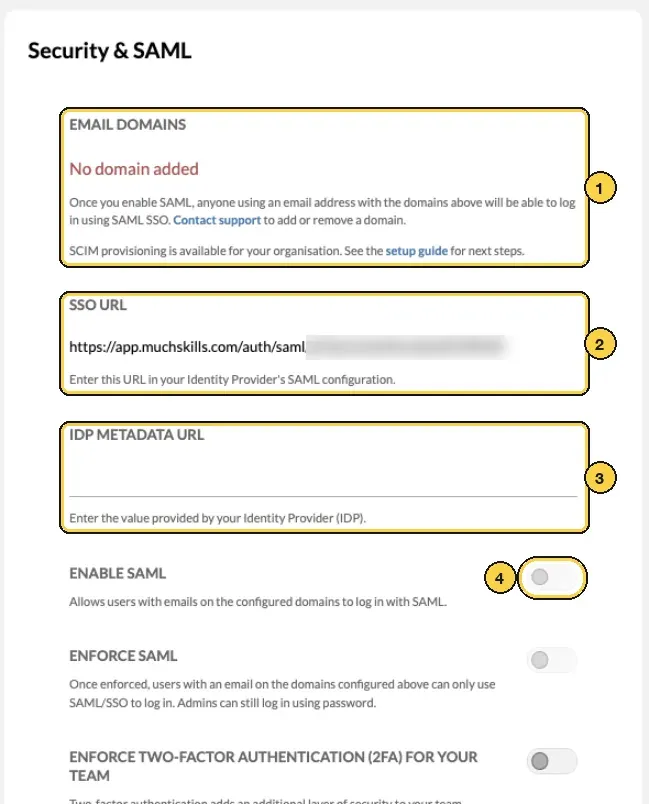
Team/Org › Settings › Security & SAML: 1 email domains, 2 SSO URL, 3 IDP Metadata URL, 4 Enable SAML.
In Google Workspace
- Add a custom SAML app. In the Google Admin console, go to Menu › Apps › Web and mobile apps and click Add app › Add custom SAML app. Enter MuchSkills as the app name and click Continue. Google's guide to custom SAML apps
- Download the IdP metadata. On the Google Identity Provider details page, download the IdP metadata file and keep it. Click Continue.
- Enter the MuchSkills values. Under Service provider details:
- ACS URL: your SSO URL.
- Entity ID: your SSO URL, the same as the ACS URL.
- Start URL: leave empty.
- Name ID format: EMAIL.
- Name ID: Basic Information › Primary email.
- Click Continue, then Finish.
- Turn the app on. Open the app, click User access, choose On for everyone or select an organisational unit, and click Save. Google says this can take up to 24 hours, though it is usually quicker.
Back in MuchSkills
- Give MuchSkills the metadata. Choose one:
- Host it yourself. Put the metadata file at an HTTPS address that MuchSkills can reach, and paste that address into IDP Metadata URL on Security & SAML. The field opens once your domain is added.
- Send it to support. Email the file to support@muchskills.com. When we have added it, the IDP Metadata URL field on your screen is filled in.
- Turn on single sign-on. Switch on Enable SAML. People with an email on your domains can now log in through Google. Until you enforce it, they can still use a password. Changes save as you make them.
- Test it. Open a private browser window and go to app.muchskills.com/login. Enter the email of a user who has the app turned on and click Continue. MuchSkills recognises the domain and shows Continue with SAML. Click it, sign in with Google, and you land in MuchSkills.
- Enforce it, if you want to. When your test users get in, turn the app on for everyone who needs MuchSkills, then switch on Enforce SAML. People on your domains can then only log in with SAML/SSO. Admins can still log in with a password. The guide Enforce single sign-on and two-factor authentication explains what changes for people.
Check it worked
- Your test user reaches MuchSkills through Google sign-in after clicking Continue with SAML.
- In Team/Org › Settings › Manage Members, people who log in with single sign-on show a SAML label next to their name.
Benefits
What you get
- One login. People use their Google Workspace account to reach MuchSkills.
- Access from the Admin console. You decide by organisational unit or access group who can use MuchSkills, under your own Google sign-in policies such as 2-Step Verification.
- Leavers lose access. Once you enforce single sign-on, a person you suspend in Google Workspace can no longer log in to MuchSkills.
Important to know
Important to know
Email addresses must match. Google sends each person's primary email as the Name ID. If it differs from the email on their MuchSkills account, MuchSkills cannot match them.
Single sign-on handles login only. It does not bring people into MuchSkills or keep their details current. Invite people, connect your HR system, or use SCIM provisioning for that.
Domains are set up by MuchSkills. We add your email domains when we configure SAML for you; admins cannot add them in the app. To add or remove a domain later, contact support. Single sign-on only applies to email addresses on the domains listed under Email domains.
Admins keep a password route. With Enforce SAML on, Admins can still log in with a password, so you are not locked out if Google sign-in has a problem. Protect those password logins with two-factor authentication.
When Google renews its certificate. The certificate is part of the metadata. When you change it in Google, download the metadata again and replace your hosted file, or send the new file to support. Then test a login.
Common errors
Troubleshooting
| What you see | Why | What to do |
|---|---|---|
| Google shows error app_not_configured_for_user | The Entity ID in Google does not match the Entity ID MuchSkills sends. It is case-sensitive | Enter your SSO URL, including your organisation's ID at the end, exactly under Service provider details |
| Google shows error app_not_enabled_for_user | The app is off for the person's organisational unit, or the change has not reached them yet | Check User access for their organisational unit, and allow time for the change |
| Google says the ACS URL in the request does not match the configured ACS URL | ACS URL in Google is not exactly your SSO URL | Copy the SSO URL from Security & SAML again and paste it into ACS URL |
| This email is not configured to use SAML/SSO | The email's domain is not listed under Email domains, or Enable SAML is off | Check the domains and the switch on Security & SAML. Ask support to add a missing domain |
| No account with this email exists | MuchSkills has no account with the email address Google sent | Check that Name ID is the primary email. Invite the person if they have no account yet |
| Enable SAML cannot be switched on | There is no domain or no IDP Metadata URL yet | Finish steps 1 and 7 first |
| This email is enforced to log in using SAML/SSO | Enforce SAML is on and the person tried a password | Click Continue with SAML and sign in with Google |
Frequently asked questions
What is the difference between Log in with Google and SAML single sign-on?
Log in with Google is on the MuchSkills login page for anyone with a Google account and needs no set-up. A custom SAML app lets you decide in the Google Admin console who can use MuchSkills, and lets you enforce single sign-on for your email domains.
Which Google role do we need?
A super administrator in the Google Admin console. In MuchSkills you need the Owner or Admin role.
Why does MuchSkills need a metadata URL when Google gives us a file?
The IDP Metadata URL field in MuchSkills reads the metadata from a web address. Google offers the metadata as a file to download, so either host the file at an HTTPS address you control, or send it to support and we add it for you.
Can we turn it on for one department first?
Yes. In the app's User access settings, turn it on for one organisational unit or an access group instead of everyone. Leave Enforce SAML off in MuchSkills while you test.
How long until the app works for our users?
Google says changes to User access can take up to 24 hours, though they usually apply sooner. Test with one user before you tell everyone.
Can people still log in with a password?
Until you switch on Enforce SAML, yes. After that, people with an email on your domains can only log in with SAML/SSO. Admins can still log in with a password.
Does single sign-on add our people to MuchSkills?
Single sign-on controls how people log in. To bring people in, invite them from MuchSkills, connect your HR system, or use SCIM provisioning from an identity provider that supports it.
We have more than one email domain. Does that work?
Yes. Ask support to add every domain your people log in with. All of them use the same custom SAML app.
Is single sign-on included in our plan?
Yes. All MuchSkills plans include single sign-on (SAML) and SCIM provisioning.